Next.js 16 · React 19 · Tailwind v4 · TypeScript strict
The admin dashboard you'd rather not build twice
Runs with zero external services — no Clerk, no Postgres, no Supabase just to open the demo. Auth, RBAC, and every state, enforced end-to-end.
No signup — pick any of the three demo accounts on the login page.
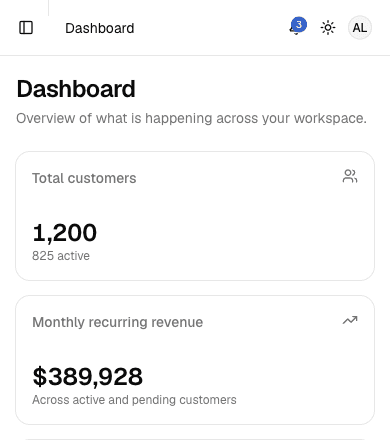
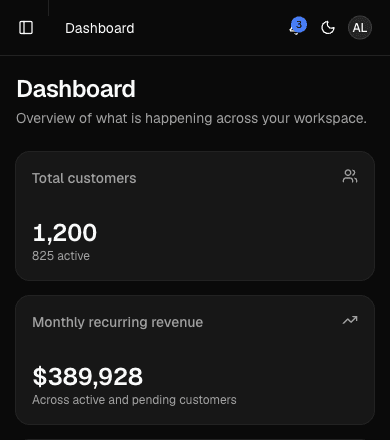
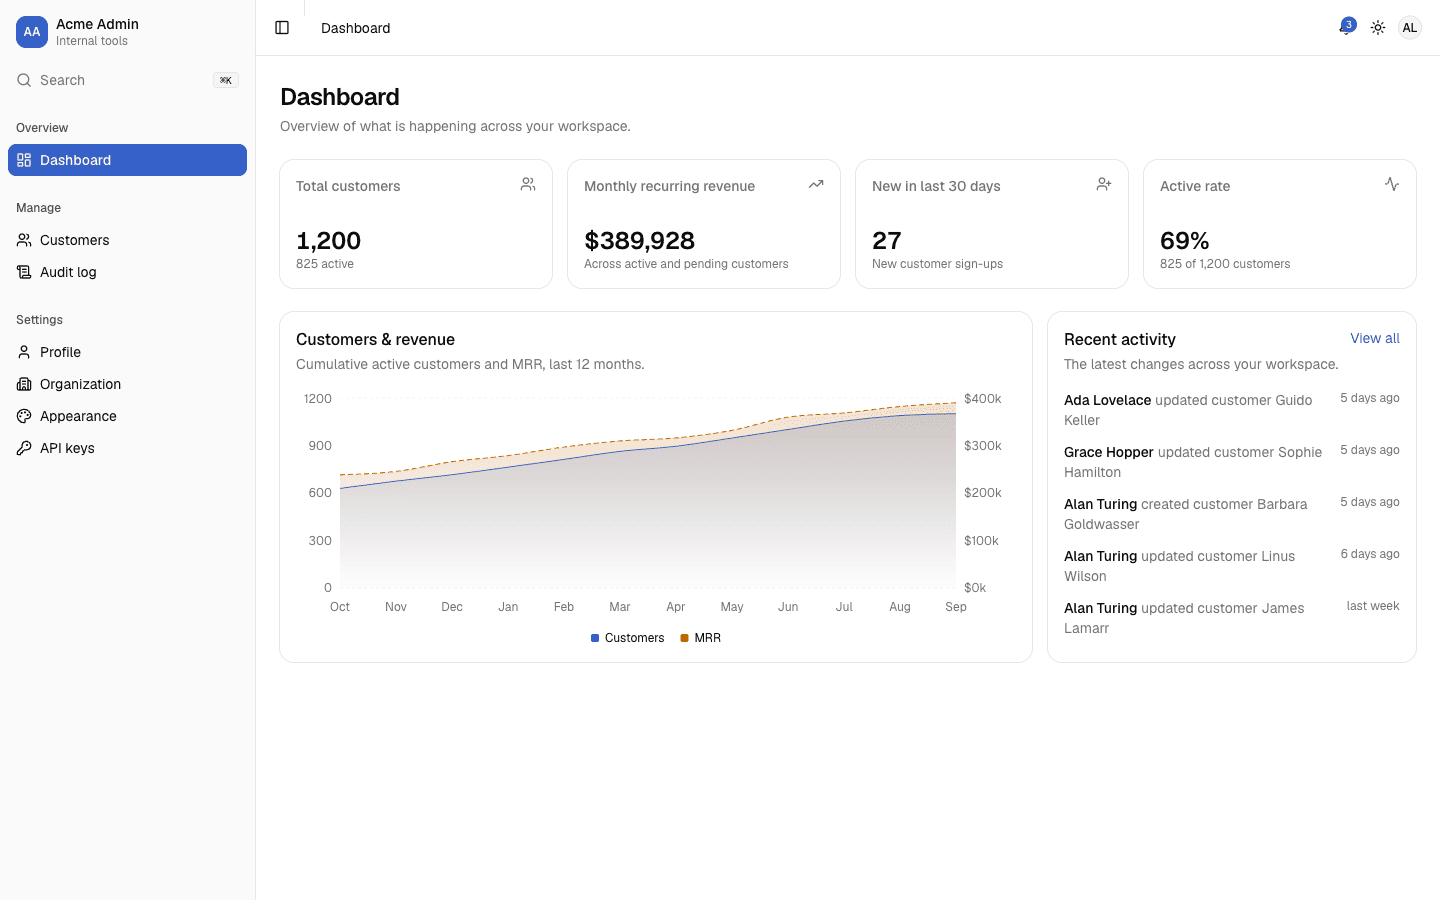
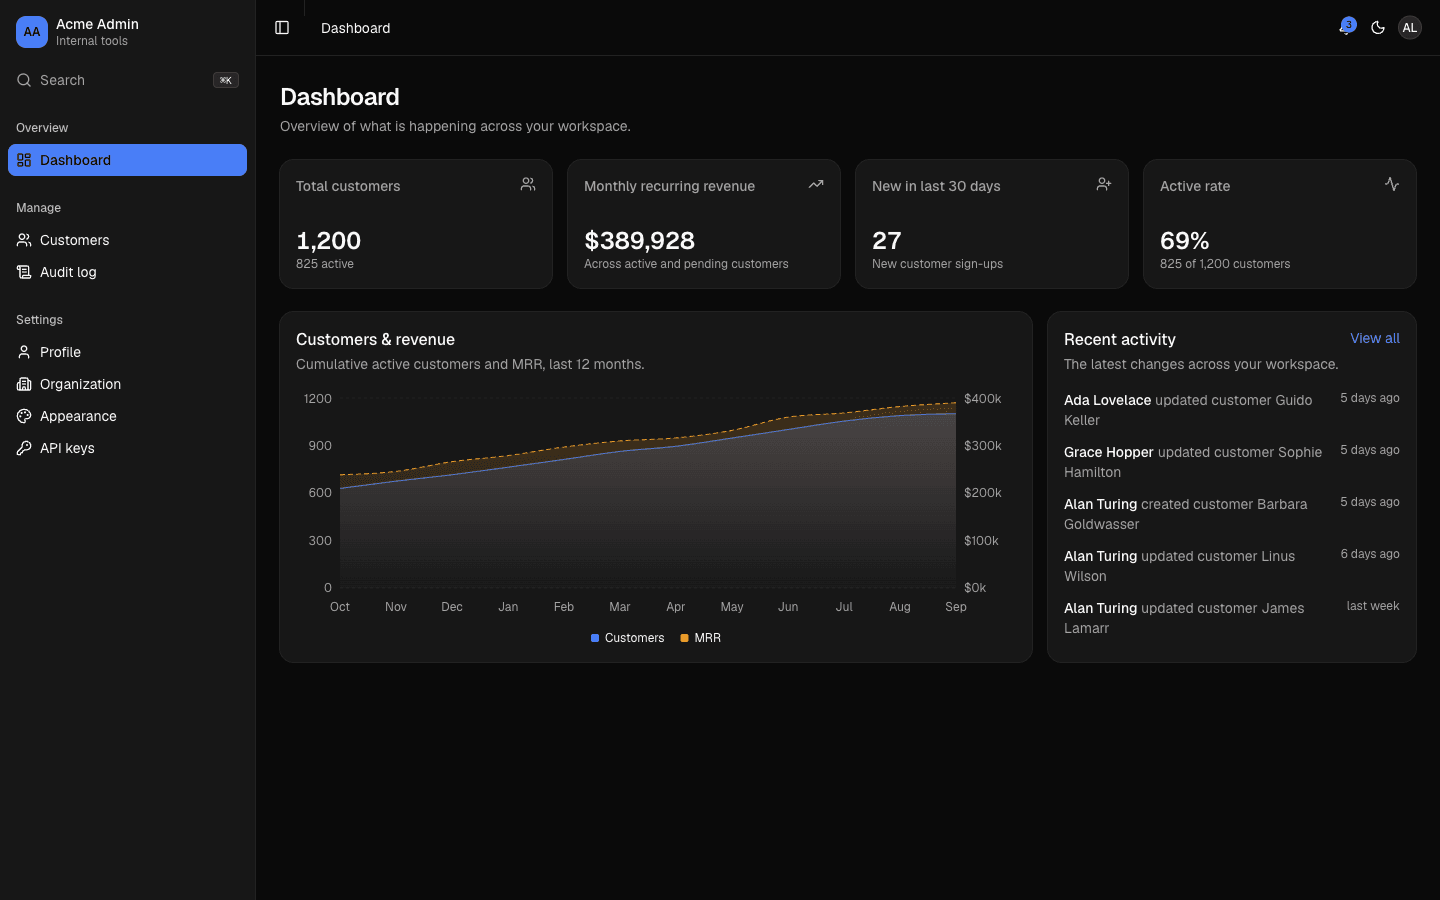
Not a claim — this is the actual app
The things every admin panel gets wrong or leaves half-done, shown straight from the repository and the running demo, not described in a bullet point.
One authorization check. Called from everywhere.
// lib/rbac/can.ts
export function can(subject: Subject, permission: Permission): boolean {
  if (!subject) return false;
  return ROLE_PERMISSIONS[subject.role]?.has(permission) ?? false;
}
Server Components, Server Actions, Route Handlers, and UI gating all call this same function — there is no second place a permission check can be forgotten.
Swap the example entity for your own — three steps, not a rewrite.
- 1. Copy the mock. Duplicate
lib/data/mock/customers.tsinto your own file, matching the shape inlib/data/repository.ts. - 2. Point the UI at it. The data table, detail page, and create/edit form already read from the repository interface — repoint them, don't rebuild them.
- 3. Go real when ready.
docs/data-layer.md, included in the purchase, walks through swapping the mock store for Supabase/Postgres behind the same interface — no page rewrites.
Same page, two roles. One server-side check decides what renders.
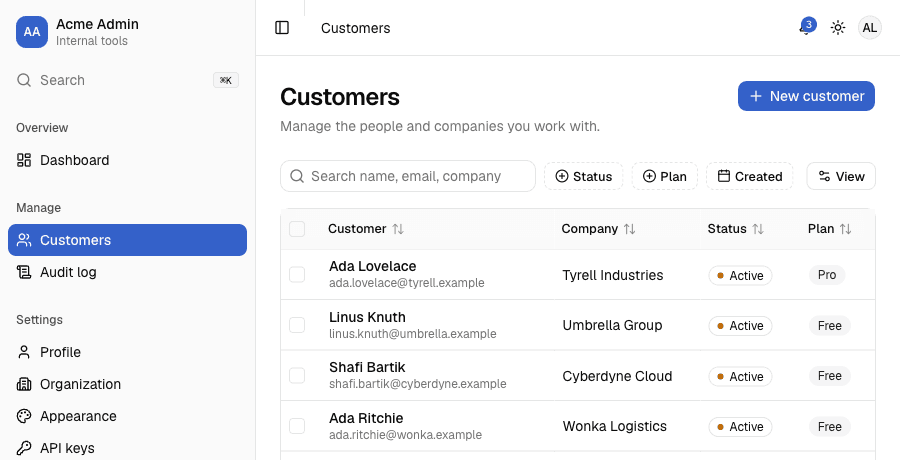
Admin — can create, bulk-select, and sees every settings page.
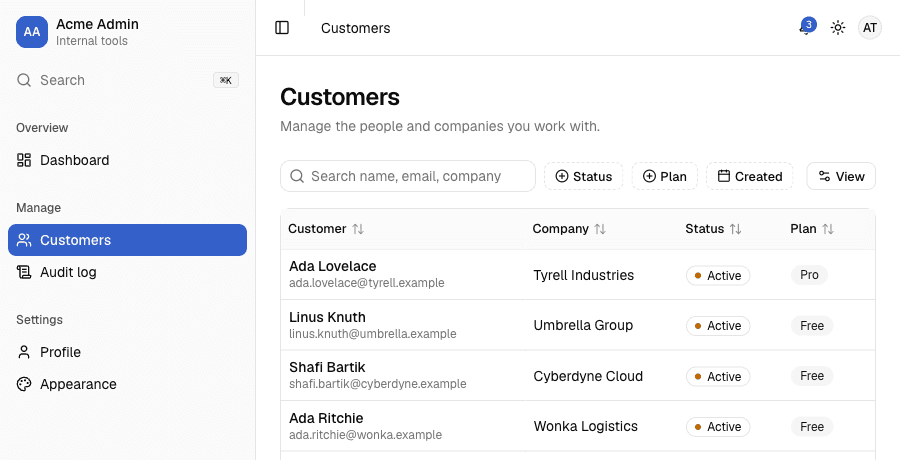
Viewer — same route, same code. No create button, no bulk actions, no Organization or API keys — Audit log stays visible, read-only, exactly matching the permission granted. The server never sends more than the role allows.
Everything the first two weeks usually cost you
Built once, correctly, so you replace the example entity with your own and ship.
Runs with zero services
No Clerk, no Postgres, no Supabase to even open the demo. An in-memory mock data layer behind a real repository interface — swap in Supabase later without touching a page.
Every state, on purpose
Loading skeletons, error boundaries, empty states, and a 403/404 for every route — an acceptance criterion here, not an afterthought discovered in production.
Themeable by design token
Rebrand by editing two files. Dark mode, three ways to switch it, and charts that recolor themselves automatically.
Auth + real RBAC
Not a nav item that hides on the wrong role, not '(planned)' — cookie sessions and permissions-as-data enforced on every Server Action and Route Handler, tested with a viewer that cannot mutate.
File upload done safely
Content-sniffed MIME validation, size limits, and a Route Handler example — never trust a filename or a Content-Type header.
Settings, API keys, audit log
Profile, organization, appearance, and a working API key example (reveal-once, revoke) — with every mutation audited.
Server-driven data tables
Real pagination, sorting, filtering, and bulk actions against 1,000+ rows — not a client-side demo table with the URL as the single source of truth, shareable and reload-safe.
Forms that validate twice
React Hook Form + Zod on the client and the server, a full CRUD example with optimistic edits, and a multi-step wizard pattern.
Notifications + command palette
An in-app inbox with optimistic read state, plus a Cmd/Ctrl+K palette that respects the current user's permissions.
Skip the two weeks. Ship your own entity by tomorrow.
Join the waitlistSimple, one-time pricing
Pay once, no subscriptions, ever. 12 months of updates included — most teams save more than the price in the first afternoon of auth and RBAC they didn't have to write. Pre-orders lock in a launch discount — payments open once the waitlist target is hit.
Personal
One developer, your own projects.
$39 once
- Unlimited personal/own-company projects
- 12 months of updates
- No client resale
Commercial
Most popularOne developer, client work included.
$79 once
- Everything in Personal
- Client projects allowed
- Per-developer license
Agency
A small team, unlimited clients.
$149 once
- Up to 10 developers
- Unlimited client projects
- Team license
A Supabase/PostgreSQL example for the mock data layer is part of the 12-month updates, whenever you're ready for it. Full terms on the license page.
Join the waitlist first
We'll email the first 50 people a launch discount before it's public.